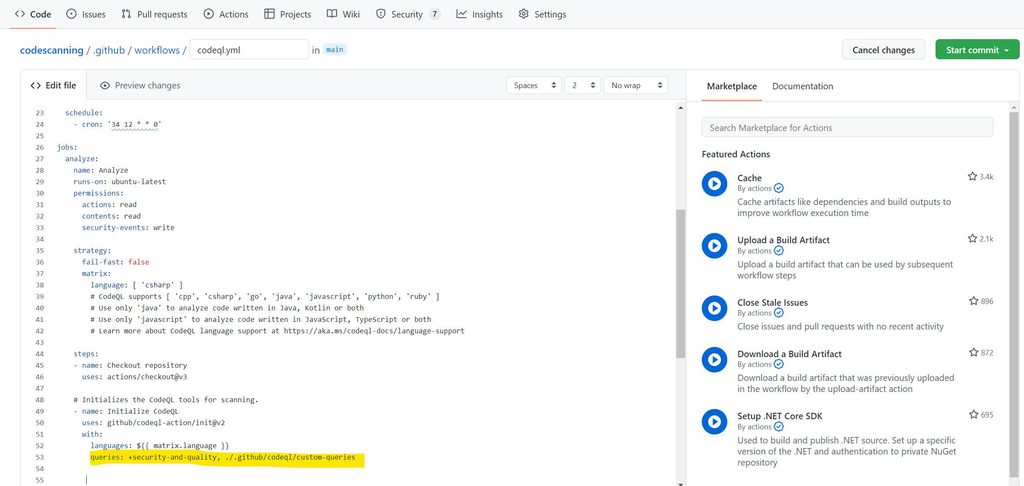
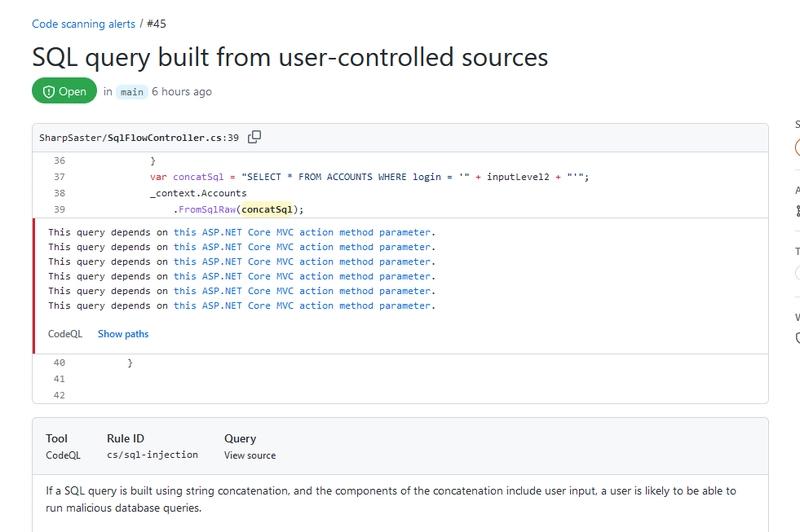
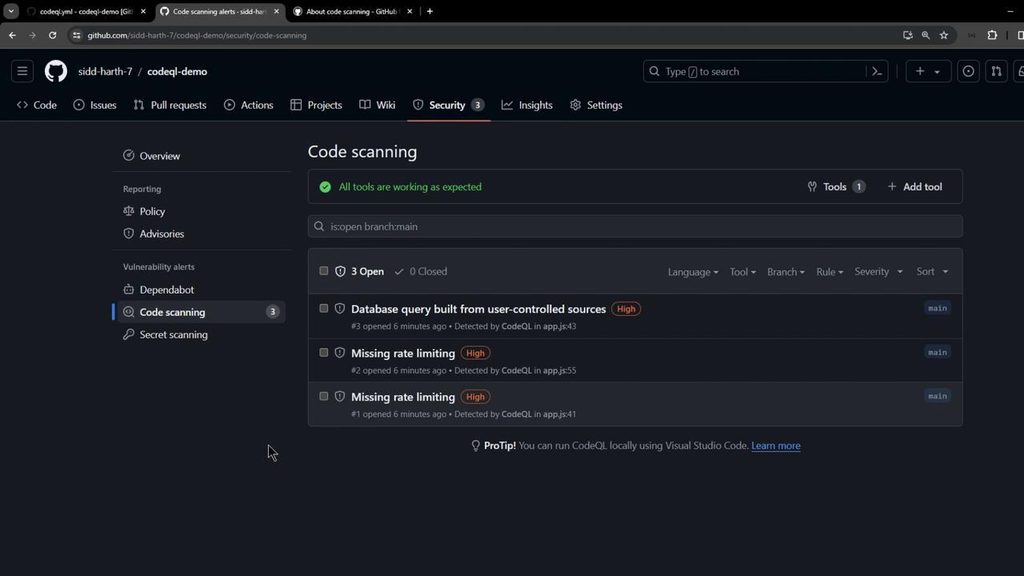
CodeQL 2.26.4 now recognizes ASP.NET Core RequireAntiforgeryToken usage correctly and reduces several C# false positives. Its GitHub Actions analysis also detects mutable references to reusable workflows and tightens event-actor validation. GitHub — 3 September 2026
- What changed: C# results should be less noisy, while some Actions workflows may receive new supply-chain alerts.
- Why it matters: Reusable workflows referenced by mutable tags can change without a repository modifying its own pipeline.
- Practical takeaway: Pin third-party actions and reusable workflows to full commit SHAs; review newly opened alerts separately from genuine regressions caused by application changes.