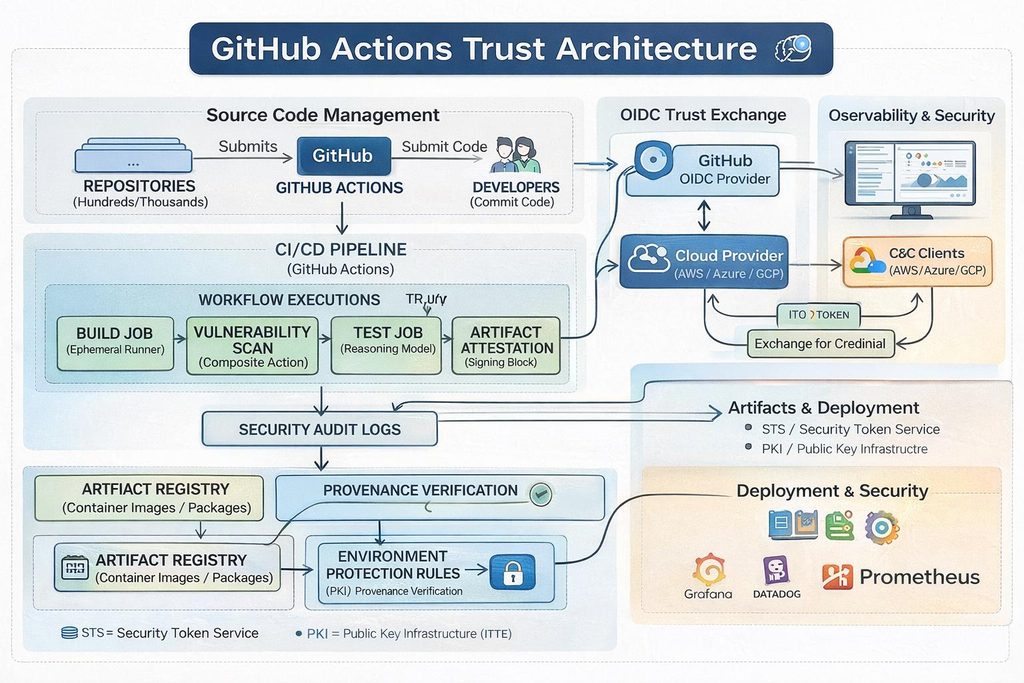
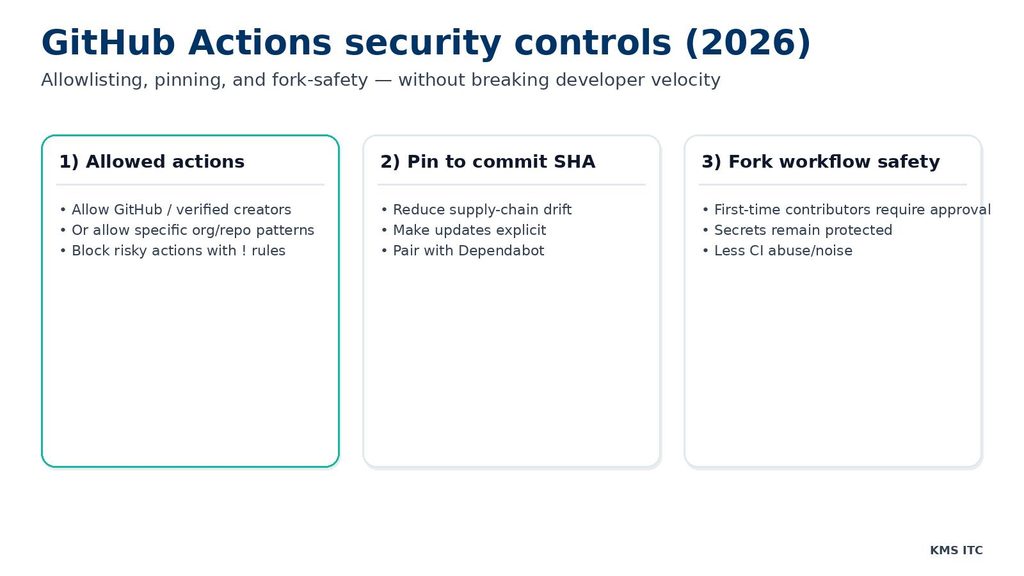
GitHub Actions can now restrict workflow execution by actor, event and individual workflow file. The generally available release adds audit insights, policy-management APIs and an evaluation mode that identifies affected runs before enforcement.
What changed
Execution protections have moved from preview to general availability for enterprises, organizations and repositories.
Why it matters
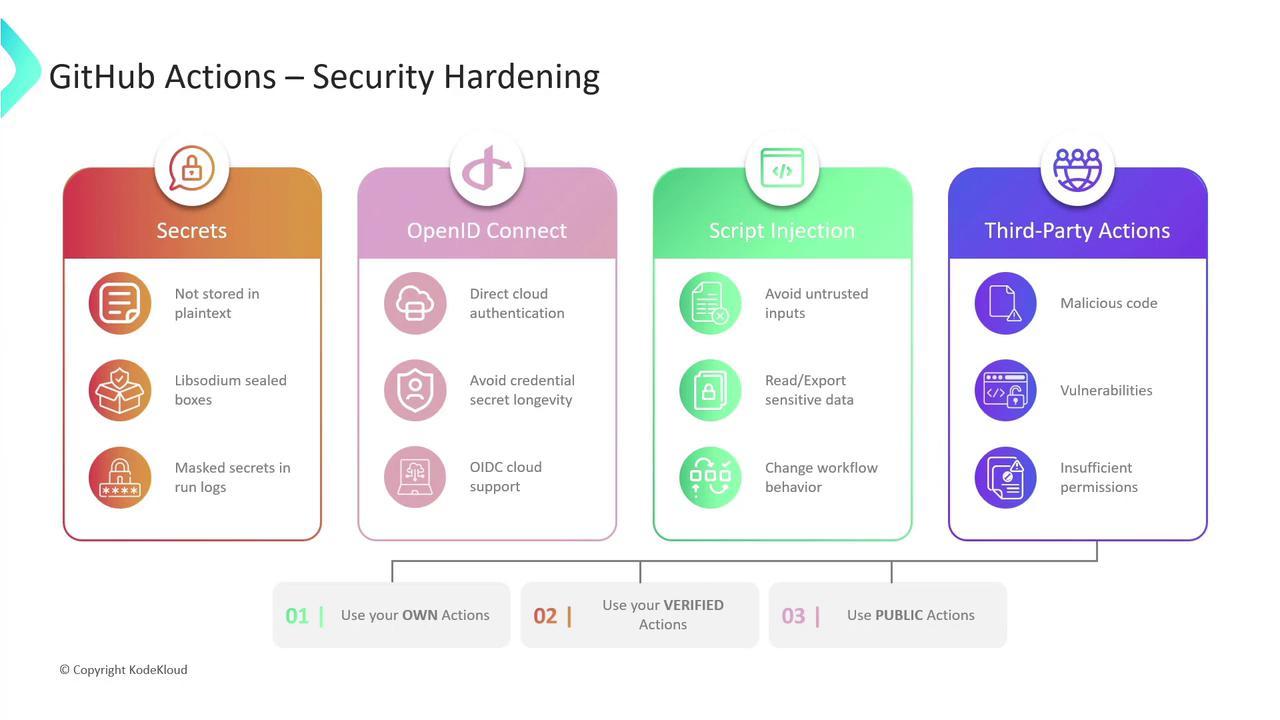
Dangerous events such as pull_request_target can expose repository secrets when untrusted fork code reaches a privileged workflow.
Practical takeaway
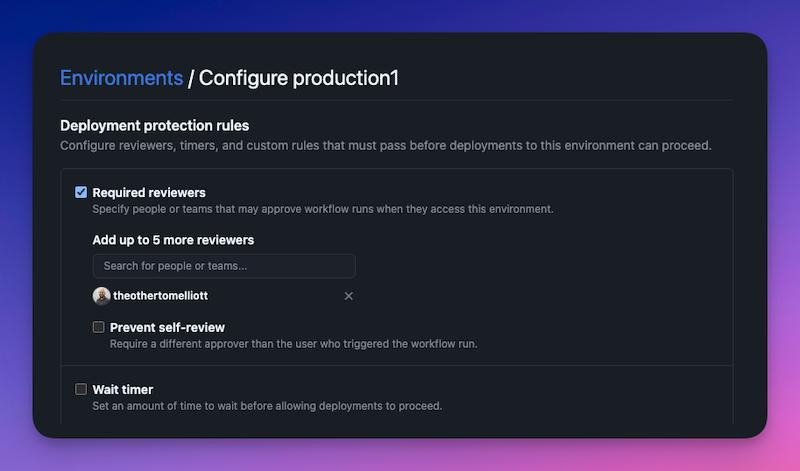
Run protections in evaluation mode, restrict deployment workflows to trusted teams and manage the resulting policies as code through the REST API.
Analysis
Policy controls reduce exposure, but workflows must still avoid executing untrusted code with write tokens or production credentials.
Published
17 September 2026